Enterprise evaluation

Operational visibility designed for enterprise security requirements.

Stereologic can be deployed on-premises or within an approved cloud environment, with non-intrusive, no-install desktop-recording software and no Administrator-level endpoint access — giving teams operational visibility while keeping processing within the agreed environment.

What reviewers ask first

Four answers that usually decide the review.

Security review tends to stall on the same four questions. These are the answers, before anyone opens a questionnaire.

No-install recording

Recording runs without installation on employee devices.

Deployment flexibility

Deploy on-premises or within the approved hosted or cloud environment.

Data stays within the deployment environment

On-premises data stays on-premises; hosted data stays within that cloud. Processing remains in jurisdiction.

No third-party AI engine calls

Operational data is not sent to an external AI engine for processing.

Security and compliance evidence

Documentation for security, privacy and procurement review.

Each item below is addressed in the Stereologic Security and Compliance Pack, provided to prospective customers on request.

SOC 2

Stereologic maintains a SOC 2 Type II attestation covering the Security, Availability, Confidentiality and Privacy trust services criteria, issued by SAV Associates Professional Corporation. A further audit period is currently in progress. The full report is available to prospective clients under NDA on request.
Availability

Availability commitments are agreed per engagement and set out in the contract, and accommodate a scheduled monthly maintenance window for platform updates. In on-premises and client-cloud deployments, availability is governed by the client’s own infrastructure.

HIPAA

Our HIPAA position and the associated documentation, including how PHI is handled in a deployment, is provided on request for covered entities and their reviewers.

Penetration testing

Penetration testing is in place, and the associated documentation is provided on request.

PII masking and sensitive-data handling

PII masking and sensitive-data handling are in place.

DPA and BAA

A data processing agreement (DPA) and a business associate agreement (BAA) are in place and available for execution.

Architecture and deployment requirements

Architecture and deployment requirements are documented and provided for technical review. Resource footprint is confirmed per deployment against your environment and observed workload during technical scoping.

SIG and CAIQ questionnaires

Standardized security questionnaires, including SIG and CAIQ, are completed where a review requires them.

Requesting the pack

This page is the evaluation layer: enough for a reviewer to decide whether Stereologic can be deployed in your environment. The pack is the procurement layer. Tell us which frameworks your review runs against and which teams need to be in the room, and we will make sure the right people are on the call.

Request the Security & Compliance Pack

Deployment architecture

How a deployment is put together.

Two things define a Stereologic deployment: where the platform runs, and what it is allowed to reach. Both are set before discovery begins.

Deployment envelope
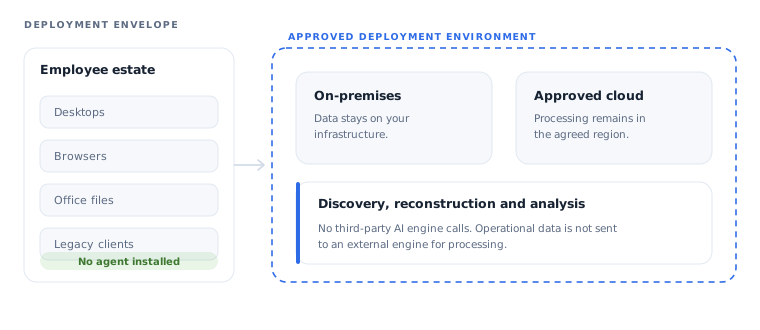
The employee estate of desktops, browsers, office files and legacy clients with no installation on them, observed by a platform running inside an approved deployment environment — on-premises, where data stays on your infrastructure, or an approved cloud, where processing remains in the agreed region — with discovery, reconstruction and analysis all inside that envelope and no third-party AI engine calls

Illustrative deployment envelope. Final architecture is confirmed per environment.

  • Nothing on the employee estate. Desktops, browsers, office files and legacy clients are observed without software installed on them, and without asking people to change how they work.
  • One deployment environment. The platform runs on your own infrastructure or within the approved hosted or cloud environment, and discovery, reconstruction and analysis all happen inside it.
  • Residency follows the deployment. On-premises data stays on-premises; hosted data stays within that cloud; processing remains in the agreed environment and jurisdiction.
  • No external AI engine. Operational data is not sent to a third-party AI engine for processing.

What is actually being observed

Reviewers usually want the scope of observation as well as the architecture. The process-level view is described on Process Mining, the task-level view on Deep Task Mining, and how the two fit together on the platform page. How personal data is handled in our own operations is set out in the privacy policy.

Security options

Three choices, made before discovery begins.

Security review is usually where operational discovery stalls. Stereologic is built so the answers are configuration choices you make, not constraints you have to accept. Each is agreed in writing and set out in the contract before any work starts.

Cloud or no cloud

Where the platform runs is your decision, not a condition of using it.

  • On-premises, entirely on your own infrastructure
  • Your cloud tenancy, in the region you specify
  • A dedicated hosted environment operated by Stereologic

AI or no AI

Whether the AI recognition layer is used at all is a choice you make per engagement.

  • AI recognition, reviewed and approved by a process engineer at defined checkpoints
  • Recognition without the AI layer, where policy does not permit it
  • Case assembly and reconstruction stay deterministic either way

American AI or international AI

Where AI is used, you choose which models are applied.

  • American models
  • International models
  • In every case, inference runs inside your approved deployment environment

Options are confirmed per environment and recorded in the contract. Deployment and model choices do not change the method: recognition is reviewed and approved before anything downstream is built on it, and case assembly, end-to-end reconstruction and map generation are deterministic by design.

Where the AI does real work

For reviewers

Nothing on this page is stronger than the pack behind it.

This page is written for an initial technical read. The Security & Compliance Pack is the source of record: it carries the current certification and attestation position, the deployment architectures, data handling and residency, PII and PHI treatment, the AI-processing boundary, and completed SIG or CAIQ responses where those are required. Where a control is in progress rather than in place, the pack says so, and audit dates are answered there rather than on this page so they stay current.

Request the Security & Compliance Pack

Take the next step

Bring your security reviewers in early.

Send the pack to the people who would otherwise stop the project in month three: security architecture, privacy, and procurement. Or bring them to the same call and let them ask directly.